
ai - 10 min read
What Mini Shai-Hulud Teaches Us About AI Supply Chain Security
The Mini Shai-Hulud worm pushed malicious npm packages with valid SLSA Level 3 attestations. Here’s why signing isn’t enough — and what defense actually requires.
26 posts in Security
The Mini Shai-Hulud worm pushed malicious npm packages with valid SLSA Level 3 attestations. Here’s why signing isn’t enough — and what defense actually requires.
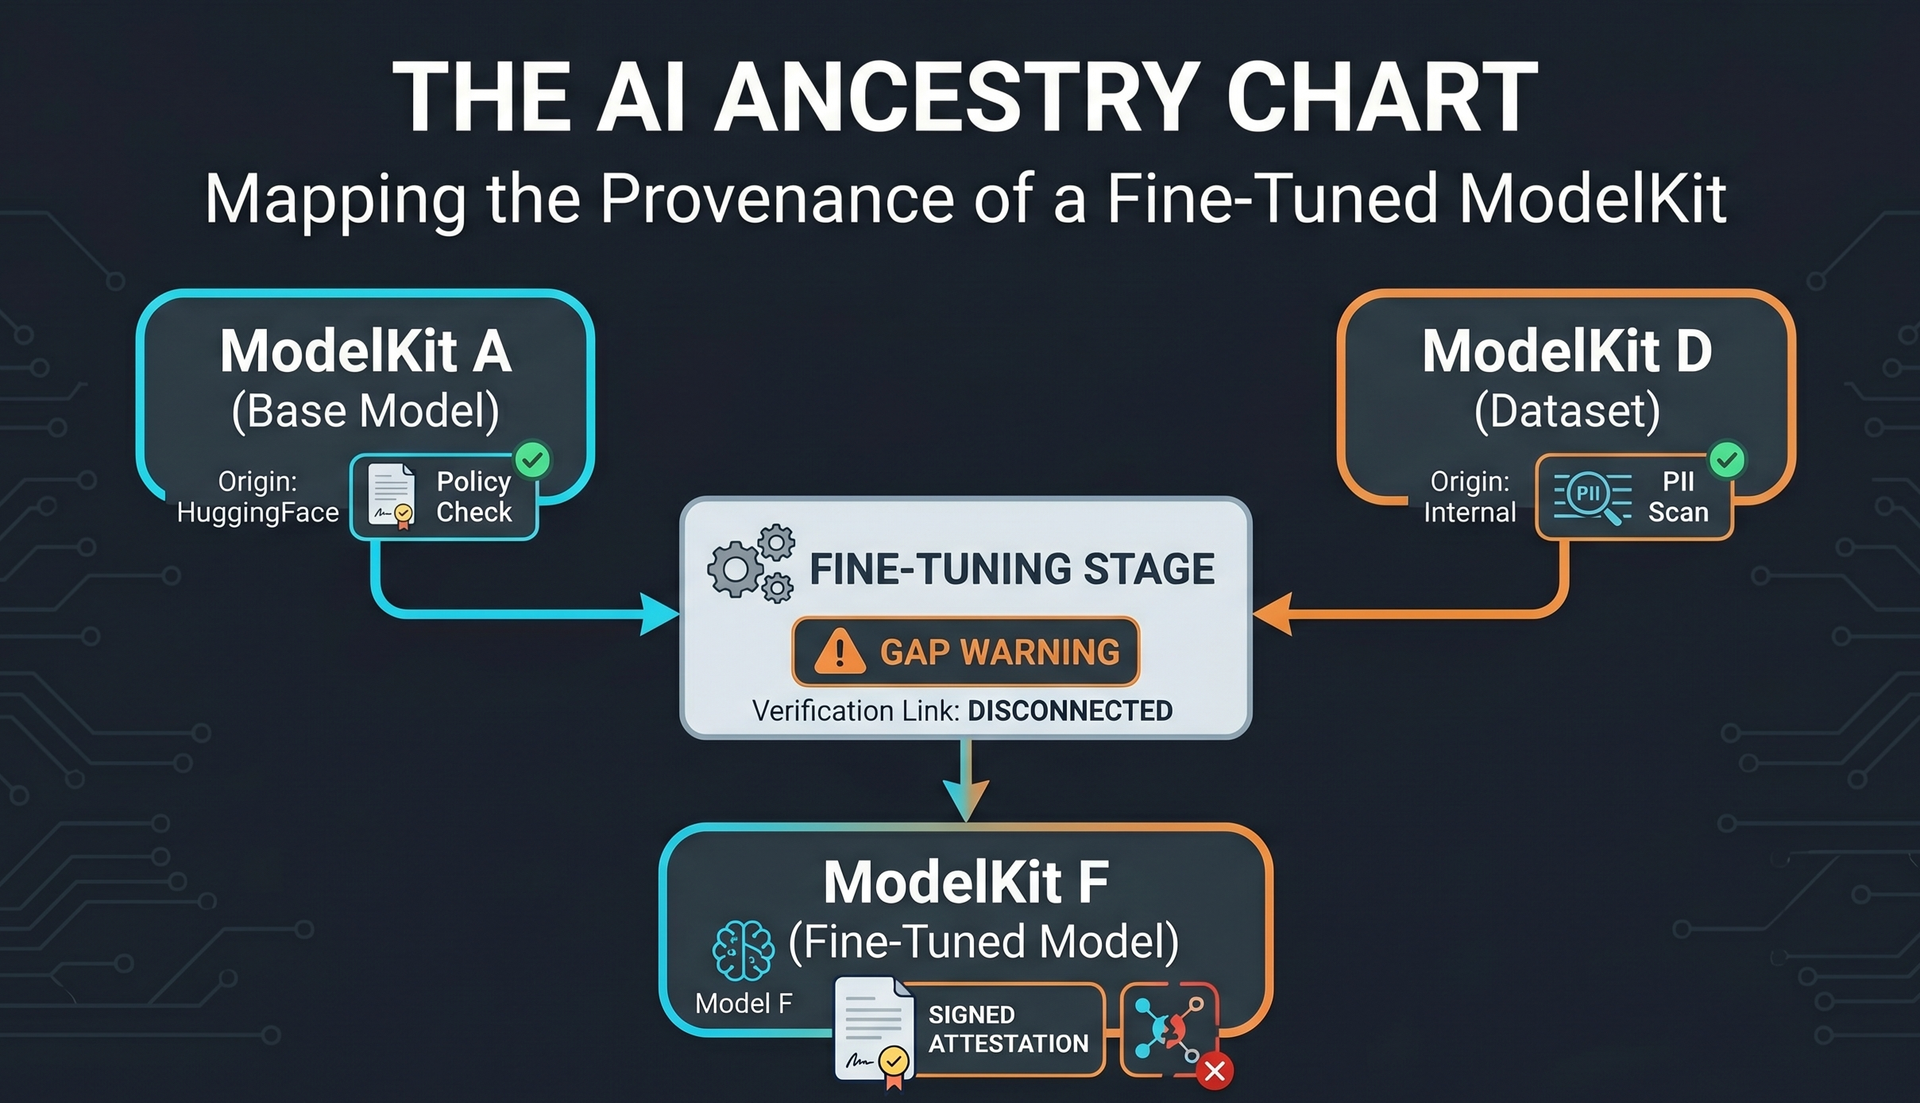
Signing your AI models isn’t enough. Learn why fine-tuned model provenance requires graph traversal, not just attestations, to close the supply chain gap.
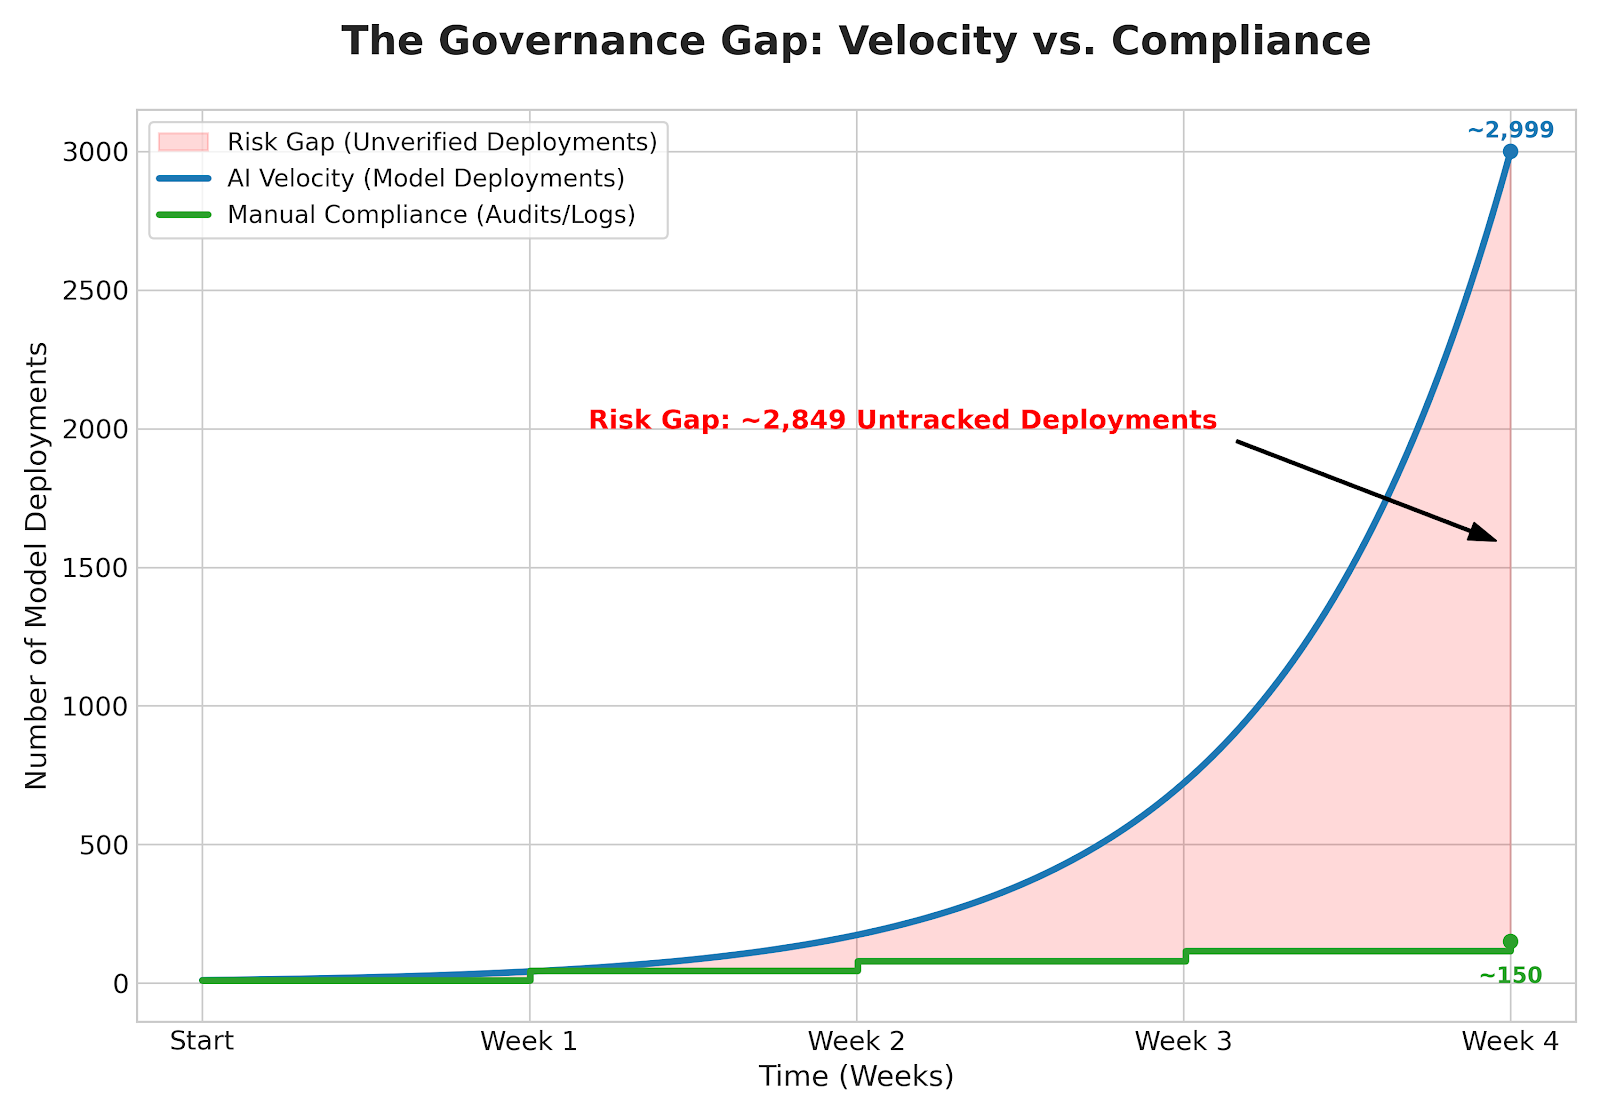
Learn how to build automated compliance gates for AI deployments using KitOps, Jozu Hub, and OPA. This tutorial walks through packaging, scanning, policy enforcement, and cryptographic attestation so every model in production can prove it belongs there.
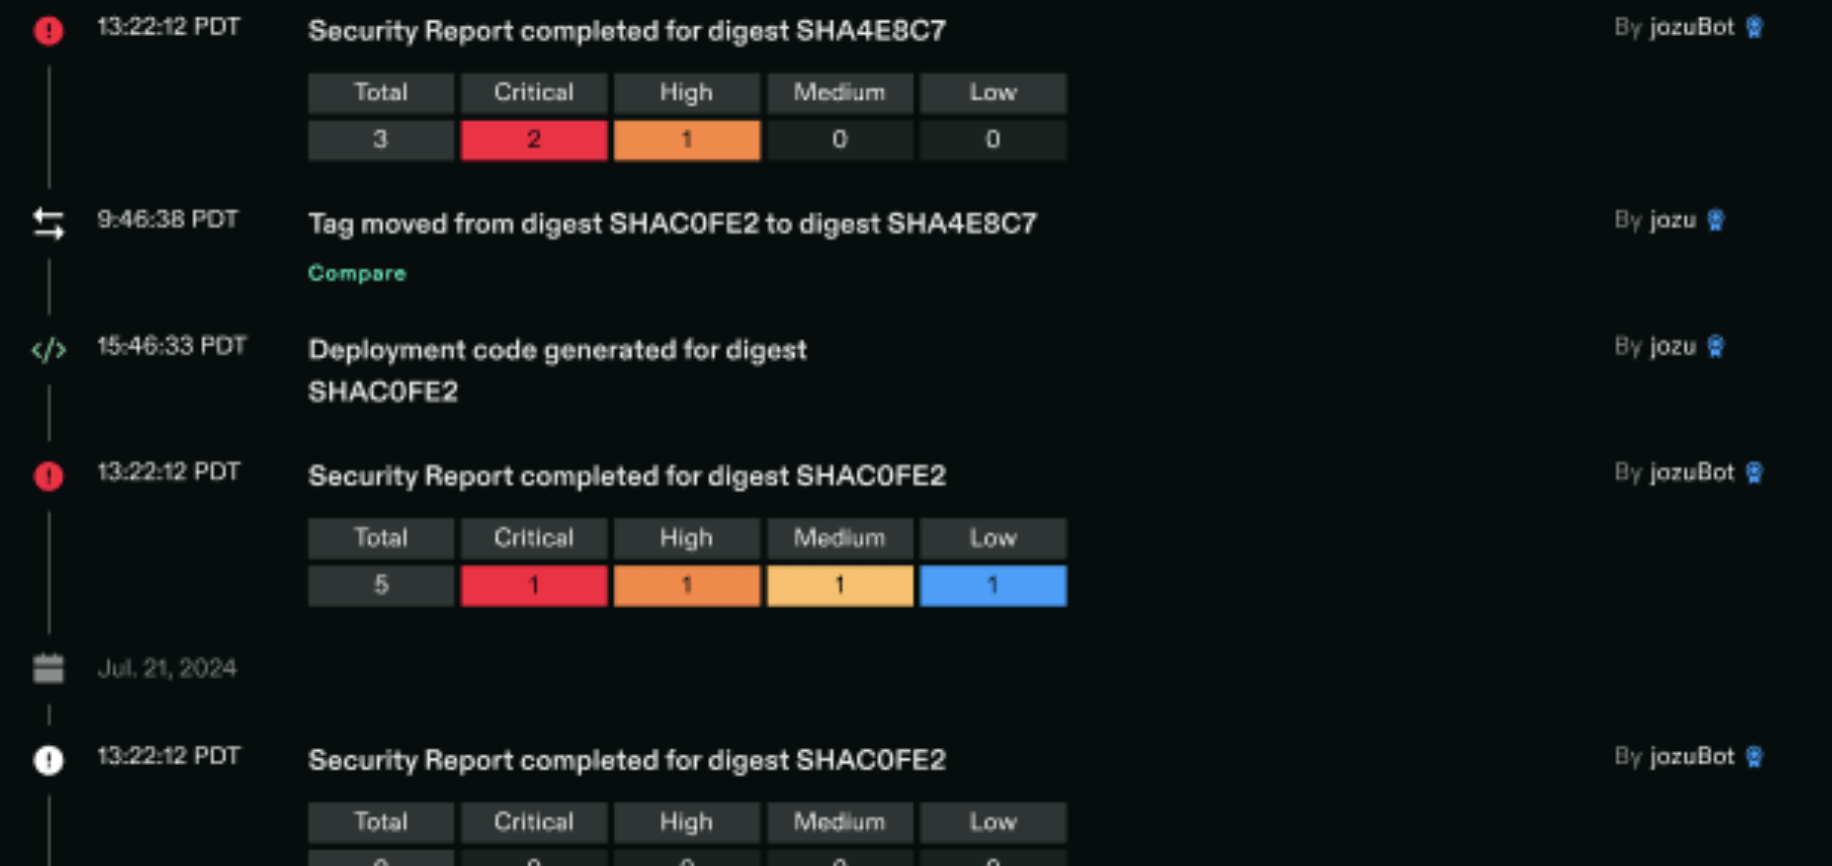
Learn how to build an end-to-end ML audit trail using MLflow for experiment tracking, KitOps for model packaging, and Jozu for centralized governance and visibility.
Hacker injects malicious data-wiping commands into Amazon’s Q AI coding assistant through GitHub pull request. Jozu releases PromptKit to prevent AI security vulnerabilities with auditable prompt management.